What happened
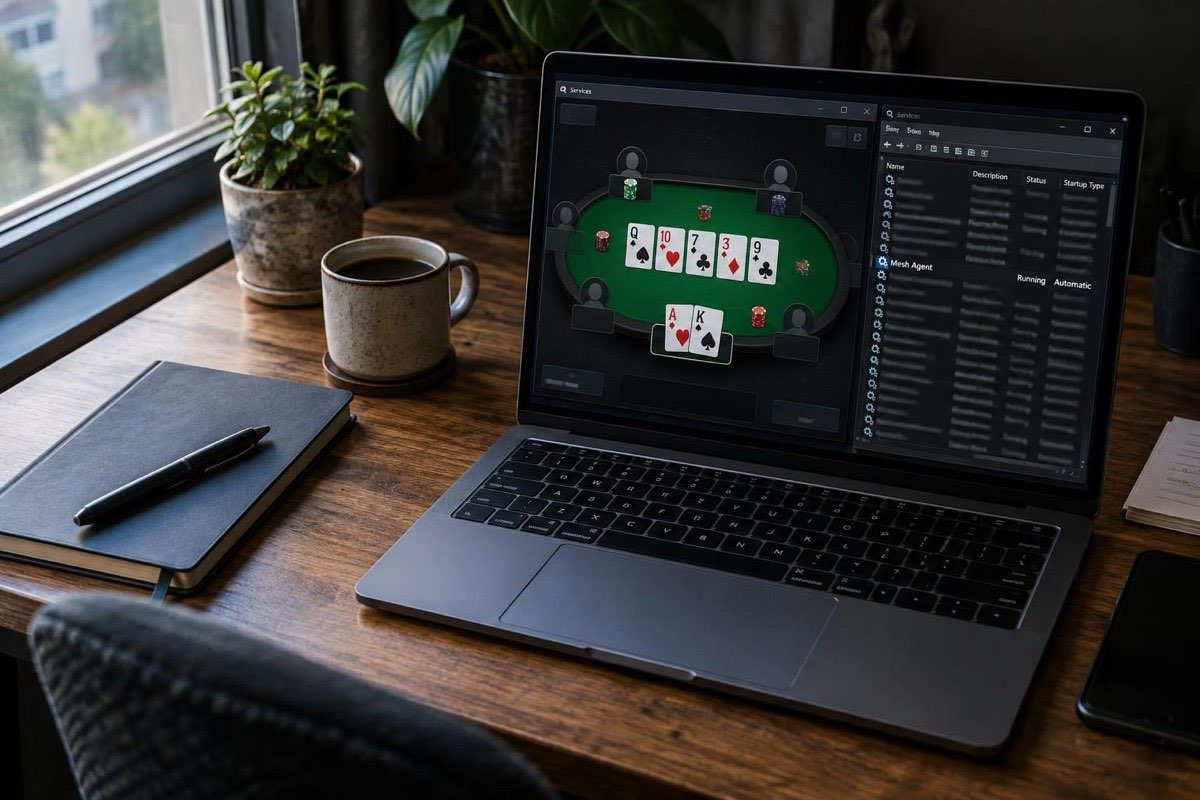
An anonymous cybersecurity account on X, @wolfsec0x0, posted that a remote-access agent was planted on high-stakes players' Windows PCs through compromised poker software. The account had 230 followers before it posted.
The claim is that the agent runs as a Windows service called "Mesh Agent," with hidden files. It can show an attacker the player's screen in real time, including hole cards. It can also take over the mouse and keyboard and reach browser passwords, session cookies and saved payment information. The account puts the number of affected players at about 30 and says the activity goes back to 2024.
No poker site and no affected player was named. The account said GGPoker and ClubWPT Gold are "not involved" and that the software vendors are responding. A commenter, Todd Witteles, noted that the compromised software is a third-party tool and not a poker platform's own client. PokerNews, which reported the story, said the community is still waiting on evidence.
Why it matters
The story is a supply-chain claim, and it has one shape: the software you installed to play better poker may have been the software that watched you play it. Nothing here is confirmed by a vendor, a site or a regulator in the reporting we could verify, and the count of about 30 players is the account's own estimate.
A separate thread on other forums has named an individual as an alleged beneficiary. That claim comes from player pattern-analysis and not from the security researcher, and no operator or authority has confirmed it. We are not repeating a name on that basis.